The Platform / Security & Compliance
Deterministic operations are materially easier to govern, audit, and certify than architectures built on probabilistic autonomous execution. The certifications follow from how XOPS works.
Certifications maintained
Information security, privacy in the cloud, AI management, and operational controls, certified to the standards enterprise risk teams already use to evaluate vendors.
ISO/IEC 27001:2022
The international standard for information security management systems. Covers policy, risk management, access control, cryptography, secure development, supplier relationships, and incident response. The 2022 revision aligns the controls catalog with modern cloud-native operations.
ISO/IEC 27018
The standard for protection of personally identifiable information processed in public cloud environments. Addresses data subject rights, consent handling, transparency of processing, retention, deletion, and breach notification, the controls regulated enterprises require from cloud-native processors.
ISO/IEC 42001
The first international standard for AI management systems, a risk-based framework for responsible AI development, deployment, monitoring, and governance. Published in 2023;
still rare among AI vendors. Maps to AI risk requirements regulators are increasingly demanding.
SOC 2
Trust services criteria covering security, availability, processing integrity, confidentiality, and privacy. Independently audited. The control posture most enterprise procurement, security, and risk teams require as table stakes before vendor onboarding.
Audit letters, scope statements, and certification details available through the Trust Center.
AI governance
ISO 42001 is a risk-based framework. The vendors that find it hardest to certify are the ones whose AI execution is fundamentally non-deterministic: outputs that vary, actions that can’t be reliably reproduced, intent that drifts.
XOPS doesn’t have that problem.
Bounded
Every action XOPS can take is defined in Configuration as Code, and the execution engine plans only against what that policy permits. Anything outside it is routed for approval or escalated, and every action is logged for audit.
Replayable
Outcome execution is reproducible. The same operational state plus the same policy produces the same plan. Audit teams can replay any production run and verify the result without re-running it against live systems.
Recoverable
Actions that can be undone are paired with their inverse, so a partial failure unwinds cleanly. Actions that can’t, such as an external notice or a shipment, require approval first or escalate under your policy. No half-states left behind for a cleanup ticket.
Ownership, not just visibility
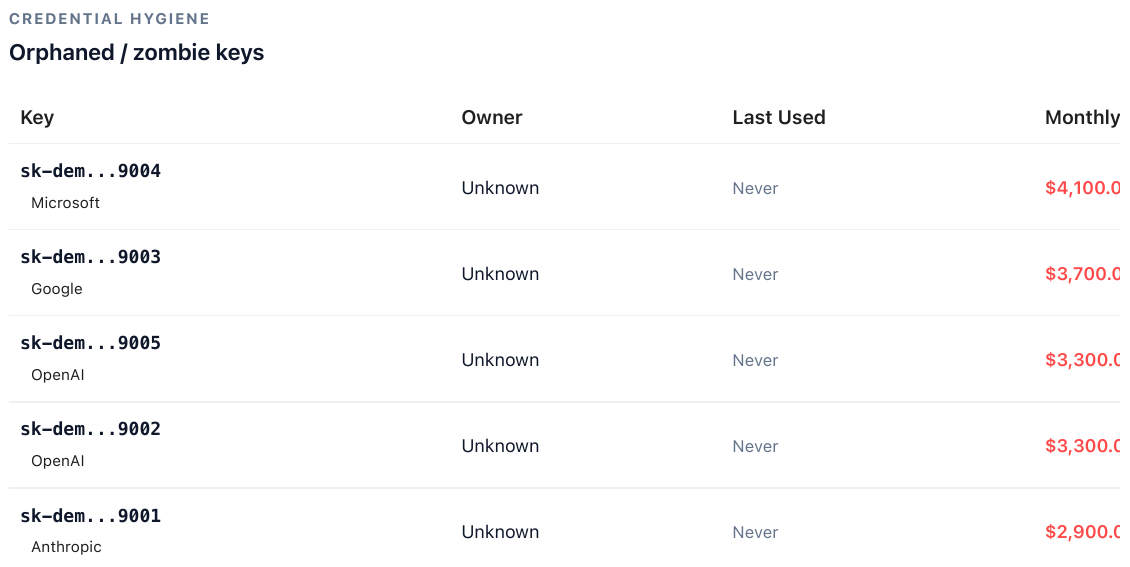
Find unowned agents and orphaned keys.
Shown: XOPS Asset Intelligence, product demo.
Audit-ready by architecture
Most enterprise estates treat audit as a forensic exercise: reconstruct what happened from per-system logs that don’t join. XOPS produces audit-grade evidence as a side effect of how it runs, not as a quarterly cleanup project.
Evidence, not assertions
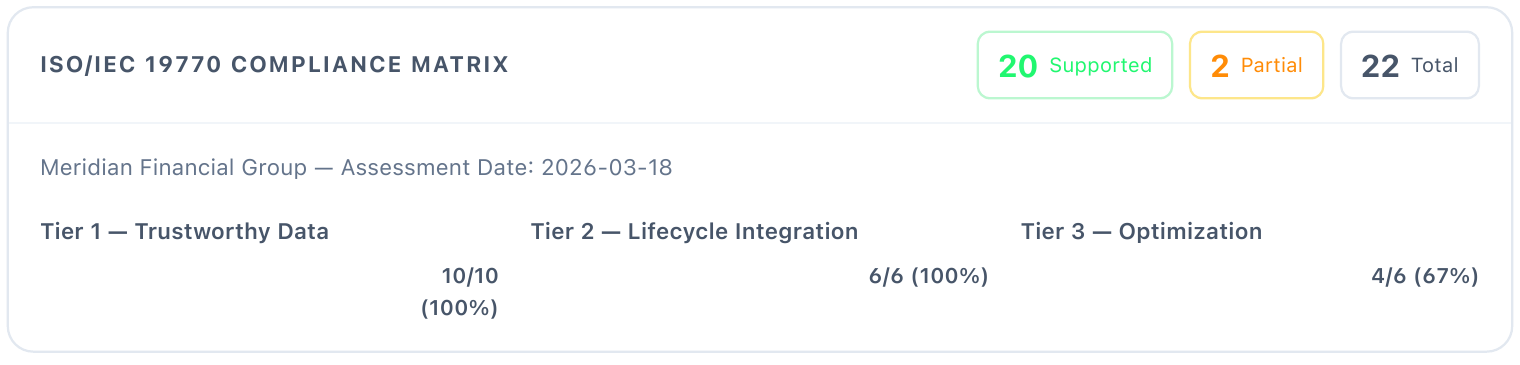
The ISO control mapping, rendered — not a spreadsheet assembled for the audit.
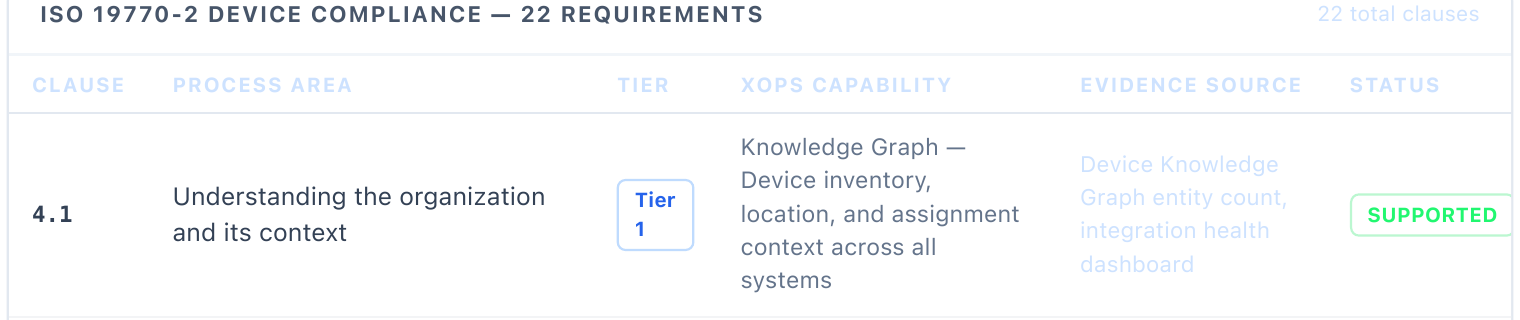
Each clause traces to a real capability and evidence source, not a checkbox.
Shown: XOPS Asset Intelligence, product demo.
For risk, security, and compliance teams
Certifications, scope statements, control mappings, and audit letters, in one place. Built for the people who have to defend it inside your enterprise.
